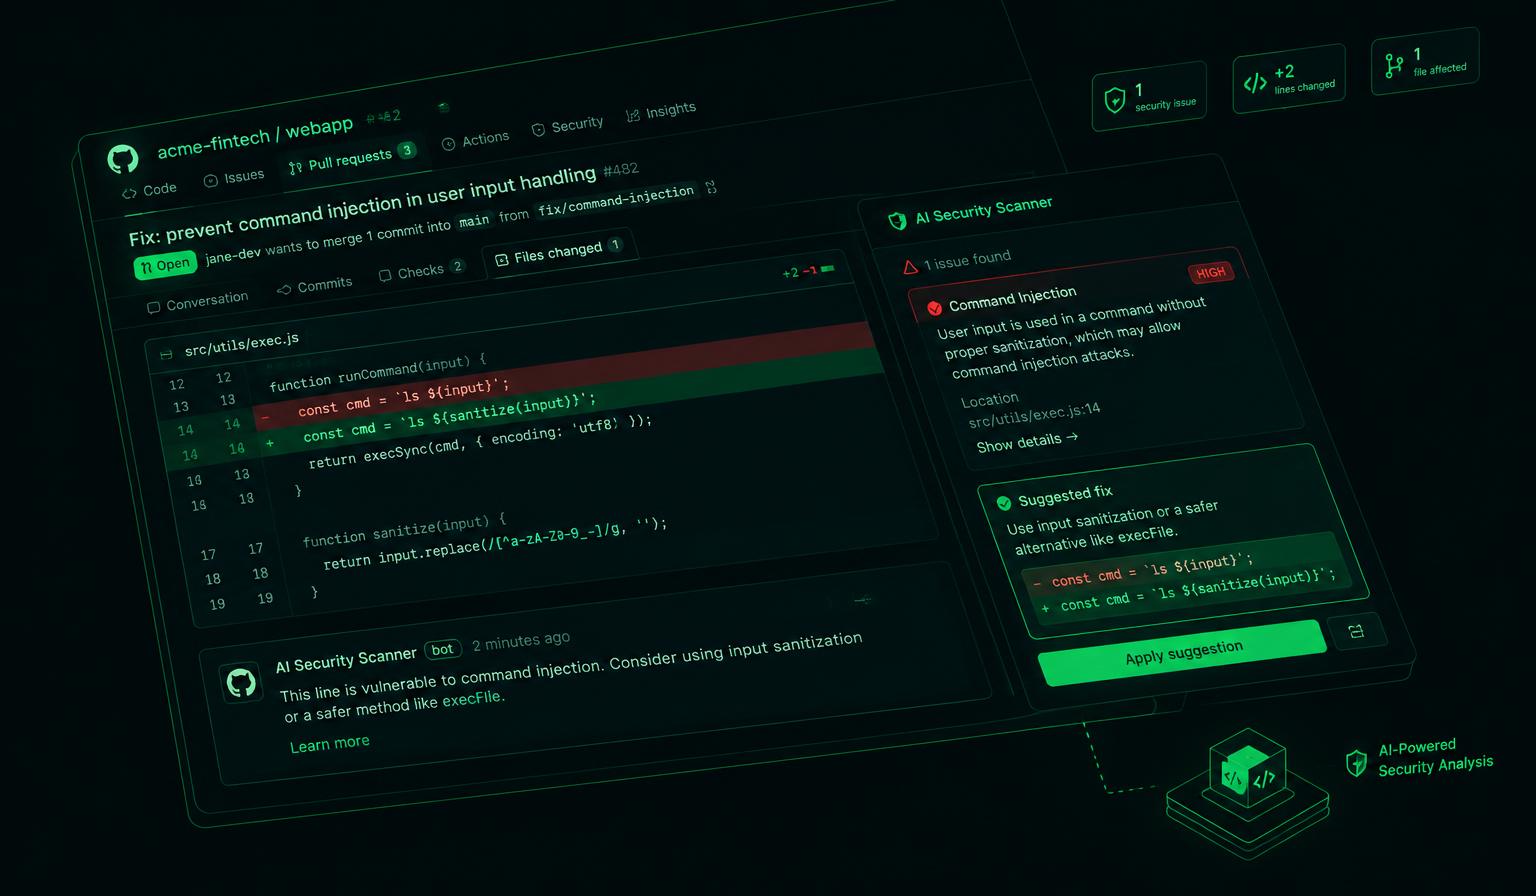
// GitHub App · DevSecOps
Your AI Security Engineer
Automatically detect logic security vulnerabilities in every Pull Request — before they get merged.
$ install --github01 / Detection
Vulnerabilities we catch
● HIGH
Broken Access Control
Missing authorization checks, IDOR, privilege escalation.
● HIGH
Business Logic Flaws
Skipped payment steps, race conditions, broken state flows.
● HIGH
Injection
SQL, NoSQL, command & template injection.
● HIGH
Auth & Session
Unverified JWTs, leaked tokens, session fixation.
● HIGH
Secrets Exposure
Hardcoded API keys and passwords in source code.
● HIGH
SSRF & Deserialization
Unauthorized internal requests, unsafe deserialization.
02 / API Docs
Fits any pipeline
Call the REST API from CI/CD, or install the GitHub App for automatic PR comments.
- POST /v1/scan
- GET /v1/scans/:id
- GET /v1/findings?repo=
- POST /v1/webhooks
curl -X POST https://api.securecode.tech/v1/scan \
  -H "Authorization: Bearer $SECURECODE_KEY" \
  -H "Content-Type: application/json" \
  -d '{
    "repo": "acme/payments",
    "pull_request": 482
  }'

# 200 OK
{
  "status": "completed",
  "findings": [{
    "severity": "high",
    "type": "broken_access_control",
    "file": "src/api/orders.ts",
    "line": 57,
    "fix": "Verify order.userId === session.userId"
  }]
}
03 / Sign up
Protect your first PR for free